

What Is the Allow Development Endpoints feature?
When Staging Protection is enabled, the staging site is locked down. This includes development endpoints like:
wp-admin/admin-ajax.php?action=debug_infowp-content/debug.logwp-includes/version.php(WordPress version info)readme.html(WordPress readme)
These endpoints are useful for development but can leak information to attackers. The Allow Development Endpoints feature selectively allows access to these endpoints while keeping the rest of the staging protection active.
Why You Need It
Development endpoints are useful for:
- Debugging: Access to error logs and debug info is essential for development
- Performance testing: Some tools need to access internal endpoints
- Migration tools: Some migration plugins use internal endpoints
- API testing: Some API testing tools need access to internal endpoints
For most staging sites, you’ll need some development endpoints accessible.
How to Allow Development Endpoints in WordPress
- Step 1
Navigate to Settings
Click into the Classic Monks plugin settings in your WordPress dashboard.
- Step 2
Go to the Security Tab
Click on the Security menu, then click the Staging Protection subtab.
- Step 3
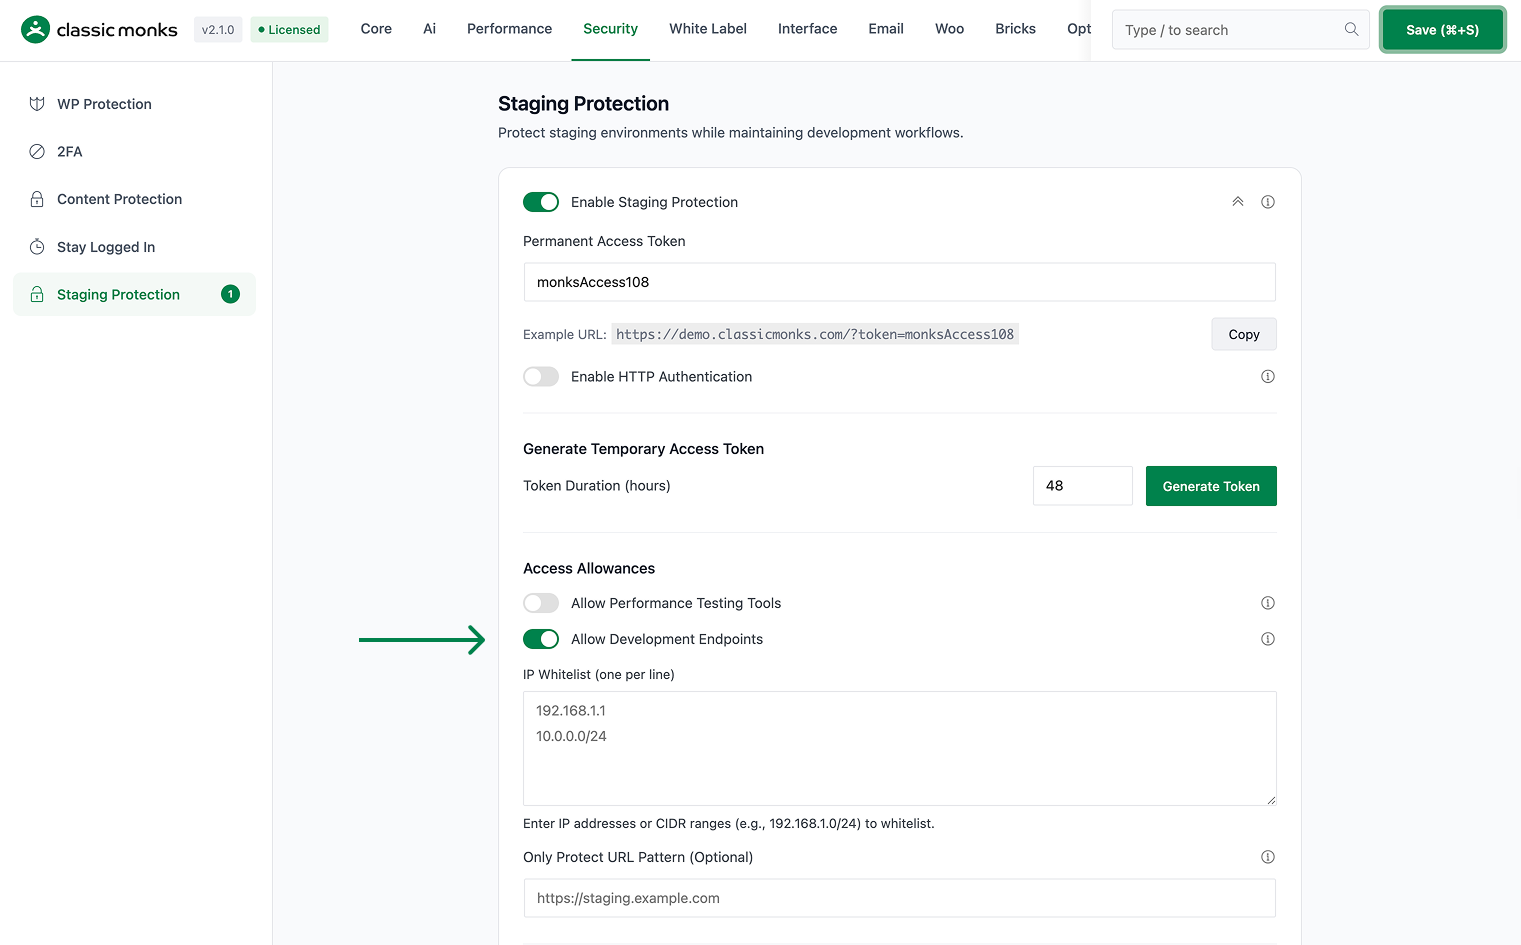
Enable Allow Development Endpoints
Scroll to Allow Development Endpoints and toggle on.
- Step 4
Save Changes
Click Save Changes.
- Step 5
Test
Try to access a development endpoint (e.g.,
wp-content/debug.log). The endpoint should be accessible.
Configuration Options
| Option | Description | Default |
|---|---|---|
| Allow Development Endpoints | Master toggle. | Off |
The whitelisted endpoints are maintained by Classic Monks. To customize, add the endpoints to your server configuration.
What Gets Affected
- The staging protection: allows access to whitelisted dev endpoints
- The development: developers can access debug info
- The user experience: dev tools work as expected
What Does NOT Get Affected
- The HTTP authentication: still applies to non-whitelisted requests
- The search engine blocking: still applies
- The staging indicator: still shows
- The regular visitors: still need authentication
Common Use Cases
API Development
When developing APIs that need to be tested, allowing dev endpoints enables direct testing without bypassing staging protection.
Migration Testing
Migration plugins often need internal endpoints to work. Allowing dev endpoints during migration is essential.
Performance Profiling
Tools like Query Monitor need dev endpoints to display database queries and PHP errors. Allow these for performance work.
Troubleshooting
4 problems and how to fix each one.
The dev endpoint is still blocked
Cause: The endpoint is not in the whitelist.
Fix: Add the endpoint to your server configuration.
The endpoint is accessible but returns 404
Cause: The endpoint path is wrong, or the file doesn’t exist.
Fix: Verify the endpoint path is correct. For example, wp-content/debug.log only works if WP_DEBUG_LOG is enabled and the log file exists.
The dev endpoint is accessible to anyone
Cause: The dev endpoint is whitelisted for all visitors.
Fix: Use the cm_staging_protection_dev_endpoint_behavior filter to set the behavior to “authenticated” for sensitive endpoints.
The dev endpoint is being accessed suspiciously
Cause: The dev endpoints can be discovered by attackers.
Fix: Use the cm_staging_protection_dev_endpoint_accessed action to log access. Monitor the logs for suspicious activity.
